Acunetix Web Vulnerability Scanner for Application Security Teams
Identify security weaknesses in websites and web applications with automated dynamic application security testing. Meteonic helps organizations in India evaluate Acunetix against their application landscape, development workflows and security objectives.
Request a Demo Talk to an AppSec Expert
What Is Acunetix?
Acunetix is a web application security testing solution associated with automated vulnerability scanning and dynamic application security testing (DAST). It helps security teams examine running websites and applications for weaknesses that could expose data, disrupt services or create paths for unauthorized access.
Use an evaluation to understand how scanning fits your application inventory, authentication flows, release cadence and remediation process. Product capabilities can vary by edition, configuration and supported technologies; confirm requirements during the demo.
Product naming note: Acunetix’s official website currently presents the product as Invicti Web + API (formerly Acunetix). Confirm current product naming, packaging and commercial availability with Meteonic before publishing.
- Automated testing of running web applications
- Findings to help teams investigate and prioritize vulnerabilities
- Support for repeatable security testing as applications change
Acunetix Capabilities to Evaluate
Assess coverage and workflow fit against your environment before choosing a web vulnerability scanner.
Web Vulnerability Scanning
Assess web applications for common vulnerability classes, including SQL injection, cross-site scripting and security misconfigurations, subject to scan configuration and technology support.
Dynamic Application Security Testing
Test applications at runtime by analyzing application behavior and responses, complementing source-code analysis and other AppSec methods.
Authenticated Testing
Discuss login workflows and protected application areas to determine the right approach for testing pages and functions that require authentication.
Actionable Findings
Review vulnerability details and available remediation guidance to help security and development teams investigate issues and plan fixes.
Repeatable Security Checks
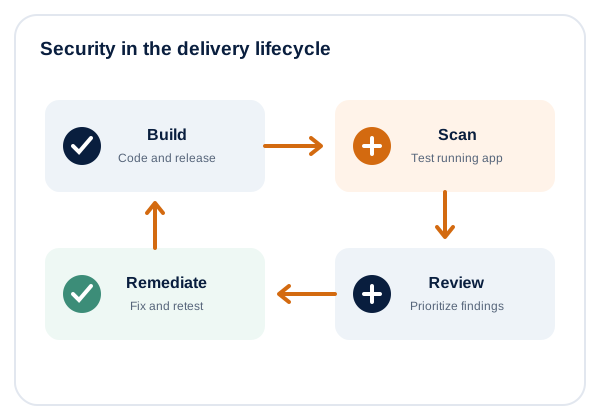
Build repeatable scanning into security routines and re-assess applications after significant changes, releases or remediation work.
Visibility and Reporting
Use scan outputs and reports to communicate findings, track open issues and support risk-based remediation discussions.
Why Use an Automated Web Application Security Scanner?
Modern applications change frequently and expose functionality through web interfaces and APIs. Manual testing remains important, but it can be difficult to repeat every check after each release. Automated DAST helps teams perform repeatable checks and improve visibility between deeper assessments.
- Expand repeatable coverage: schedule scans for in-scope applications and environments.
- Prioritize investigation: use severity, evidence and business context to plan remediation.
- Support DevSecOps: assess where security testing can fit into development and release workflows.
Who Should Evaluate Acunetix?
Application Security Teams
Improve visibility into web application weaknesses and coordinate remediation with engineering.
Development Leaders
Explore repeatable security checks that fit release processes and development priorities.
Security Consultants
Evaluate automated scanning as one part of a broader assessment and testing toolkit.
Digital Businesses
Assess customer-facing websites, portals and business-critical web applications.
Evaluate Acunetix with Meteonic in India
Meteonic helps organizations assess security tools against technical requirements, application architecture and operational workflows. Our team can discuss your target inventory, scan frequency, authentication requirements, reporting needs and integration considerations before you decide on the next step.
Ask for a product demonstration to explore suitability for your use case. Product availability, packaging and capabilities should be confirmed during the evaluation.
Request an Acunetix DemoPrepare for your demo
- Number and type of web applications
- Authenticated and public-facing application scope
- Preferred scan cadence and environments
- Reporting and workflow requirements
- Current application security testing process
Frequently Asked Questions About Acunetix
Improve Visibility into Web Application Risk
Talk to Meteonic about evaluating Acunetix for your application security program.
Request a DemoTalk to an Expert