Mobile Application Security Testing Tools
Find mobile app vulnerabilities before attackers do. Test Android and iOS applications for code, data, API, runtime, authentication, privacy and tampering risks.
Build a repeatable mobile application security testing program aligned with the OWASP MASVS and MASTG, from development to production.
What is Mobile Application Security Testing?
Mobile Application Security Testing (MAST) is the process of evaluating Android and iOS applications for security and privacy weaknesses using techniques such as static analysis, dynamic analysis, penetration testing, runtime testing and API assessment. It helps identify risks in application code, local storage, authentication, cryptography, network communication, platform interaction, privacy controls and resistance to reverse engineering or tampering.
Why Mobile Application Security Testing Matters
Mobile apps expose a unique combination of client-side code, device data, platform services, APIs and backend systems.
Protect Sensitive Mobile Data
Identify insecure local storage, exposed secrets, weak cryptography and unintended data disclosure on mobile devices.
Test Authentication & Authorization
Assess login, session handling, authorization logic, biometric flows and controls protecting sensitive functions.
Secure APIs & Network Traffic
Validate mobile-to-server communication, TLS configuration, certificate validation and API exposure.
Analyze App Code & Binaries
Inspect application packages and security-relevant implementation patterns for Android and iOS.
Resist Tampering & Reverse Engineering
Evaluate protections against debugging, tampering, hooking, repackaging and reverse-engineering attempts.
Secure Every Release
Integrate mobile security checks into CI/CD so teams can identify issues earlier and repeat testing consistently.
Test the Complete Mobile Application Attack Surface
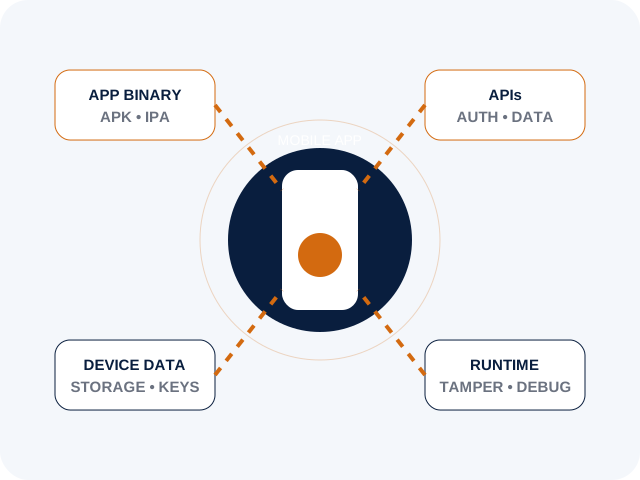
A strong mobile application security program should not stop at source-code scanning. Mobile applications combine client-side logic with operating-system features, local storage, third-party SDKs, network services and backend APIs.
Application Binary
Analyze packaged Android and iOS applications for security weaknesses.
Local Storage
Check sensitive information, credentials, tokens and cryptographic material stored on devices.
Network Layer
Validate secure transport, certificate handling and protection against traffic interception.
Backend APIs
Assess APIs used by the mobile application for authentication, authorization and data exposure risks.
Mobile Application Security Testing Capabilities
Combine automated assessment with deeper testing where application risk requires it.
Static Application Security Testing
Inspect application code and compiled binaries for insecure implementation patterns, exposed secrets, weak controls and mobile-specific weaknesses.
- Android APK/AAB assessment
- iOS IPA assessment
- Code and binary analysis
- Third-party component visibility
Dynamic Mobile App Security Testing
Observe application behavior during execution to identify runtime weaknesses, insecure communication and security-control failures.
- Runtime behavior analysis
- Authentication testing
- Network traffic assessment
- Runtime security checks
Mobile Application Penetration Testing
Use expert-led testing to investigate business logic, platform interaction and vulnerabilities that automated analysis may not fully understand.
- Manual validation
- Business logic testing
- Client-server assessment
- Exploitability validation
Mobile API Security Testing
Assess APIs that carry authentication, transactions and sensitive application data between mobile clients and backend services.
- Authorization testing
- Authentication controls
- Input validation
- Data exposure
Runtime Application Protection
Evaluate and strengthen protections that operate while the application is running against suspicious activity and runtime manipulation.
- Anti-tampering
- Anti-debugging
- Root/jailbreak detection
- Runtime threat controls
Continuous Mobile Security
Automate security checks throughout the application lifecycle and establish repeatable release-gate processes.
- CI/CD integration
- Build-time checks
- Security reporting
- Remediation workflows
Align Mobile Security Testing With OWASP MASVS
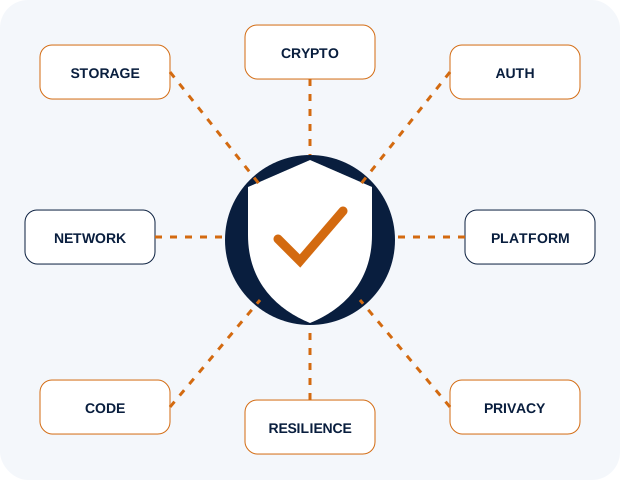
The OWASP Mobile Application Security Verification Standard (MASVS) defines security control groups for mobile applications. The OWASP Mobile Application Security Testing Guide (MASTG) provides testing processes, techniques and test cases for evaluating those controls.
MASVS-STORAGE
Protection of sensitive data stored on the device.
MASVS-CRYPTO
Correct use of cryptographic functionality.
MASVS-AUTH
Authentication and authorization controls.
MASVS-NETWORK
Secure communication with remote endpoints.
MASVS-PLATFORM
Secure interaction with mobile platforms and apps.
MASVS-RESILIENCE
Resistance to reverse engineering and tampering.
MASVS-PRIVACY
Controls supporting protection of user privacy.
MASVS-CODE
Secure code and application maintenance practices.
Mobile Security Testing vs Other Application Security Testing
| Approach | Primary Focus | Mobile-Specific? | Typical Value |
|---|---|---|---|
| Mobile Application Security Testing | Mobile code, binary, runtime, storage, platform and API risks | Yes | Mobile attack-surface visibility |
| SAST | Source or code-level weaknesses | Not necessarily | Early developer feedback |
| DAST | Running application behavior | Not necessarily | Runtime vulnerability discovery |
| Penetration Testing | Human-led security investigation and exploitation | Can be | Deep validation and business-logic testing |
These approaches can complement one another. OWASP describes mobile security testing as covering static and dynamic analysis and notes that mobile assessments commonly involve the client-server architecture and backend APIs as well.
What Should Mobile Application Security Testing Detect?
Insecure Data Storage
Sensitive information stored insecurely on the device.
Weak Authentication
Authentication and session-control weaknesses.
Broken Authorization
Improper access controls and privilege enforcement.
Insecure Network Communication
Weak transport protection and certificate-validation issues.
Hardcoded Secrets
Credentials, keys or sensitive configuration exposed in the application.
Reverse Engineering
Application logic and intellectual property exposed through analysis.
Tampering
Unauthorized modification or repackaging of application binaries.
Runtime Manipulation
Debugging, hooking and runtime manipulation risks.
Privacy Weaknesses
Unnecessary collection, exposure or handling of sensitive user data.
A Practical Mobile App Security Testing Workflow
Discover
Identify applications, versions, platforms, APIs, dependencies and critical data flows.
Assess
Run static, dynamic and API security checks against relevant mobile attack surfaces.
Validate
Prioritize meaningful findings and validate exploitability or runtime impact where appropriate.
Remediate & Retest
Fix weaknesses, integrate security gates and repeat testing before release.
Mobile Application Security Testing Tools in India
Organizations in India can use mobile application security testing tools to assess Android and iOS applications across development, pre-release and production security programs. A practical evaluation should consider application architecture, APIs, compliance requirements, CI/CD integration, testing depth, reporting, deployment model and support for the technologies used by the business.
For regulated and high-value mobile applications, combine automated assessment with appropriate manual security validation rather than relying on a single security test.
How to Choose Mobile Application Security Testing Tools
1. Android & iOS Coverage
Verify support for the platforms, frameworks and application formats used by your teams.
2. Static & Dynamic Testing
Look for coverage across binaries, runtime behavior and backend communication.
3. OWASP MASVS Alignment
Check how results map to recognized mobile security controls and testing guidance.
4. API Security
Ensure the platform can assess APIs that support critical mobile workflows.
5. CI/CD Integration
Automate repeatable checks so mobile security becomes part of release engineering.
6. Runtime Protection
For high-risk applications, evaluate runtime defenses against tampering and manipulation.
7. Reporting & Remediation
Prioritized findings, evidence and actionable remediation guidance reduce security-team friction.
8. Enterprise Scale
Consider integrations, deployment, access controls, reporting and support for multiple teams and applications.
Mobile Application Security Topics We Cover
Mobile Application Security Testing Solutions from Meteonic
Meteonic helps organizations evaluate and deploy enterprise mobile application security technologies for Android and iOS environments. Our approach can combine vulnerability assessment, application testing, runtime security and continuous monitoring according to the application's risk profile.
With 18+ years of experience and 300+ unique clients including Fortune 500 organizations, Meteonic supports security and engineering teams with enterprise-focused cybersecurity and DevSecOps solutions.
Ask for a Free Demo
Questions Security Leaders Ask About Mobile App Security
What are mobile application security testing tools?
They are technologies used to identify security and privacy weaknesses in mobile applications through static analysis, dynamic analysis, penetration testing and related assessment techniques.
How do I test an Android app for security?
Assess the Android application binary and runtime behavior, local storage, authentication, network communication, APIs, platform interaction and resilience controls using appropriate automated and manual techniques.
How do I test an iOS app for security?
Evaluate the iOS application binary, runtime behavior, data storage, authentication, network communication, APIs, platform controls and resistance to tampering and reverse engineering.
What is the difference between MAST and mobile penetration testing?
MAST is the broader practice of testing mobile application security using multiple techniques. Mobile penetration testing is a human-led assessment that can form part of a MAST program.
What is OWASP MASVS?
OWASP MASVS is a security verification standard for mobile applications that organizes important mobile security controls and provides a baseline for assessment.
What is OWASP MASTG?
OWASP MASTG is a comprehensive testing guide describing processes, techniques and test cases for mobile application security testing.
Can mobile security testing check APIs?
Yes. Mobile applications commonly depend on backend APIs, so security testing should evaluate authentication, authorization, input handling and sensitive-data exposure in those interfaces.
When should mobile app security testing be performed?
Testing can be integrated throughout the development lifecycle and repeated before releases and after meaningful changes. Higher-risk applications may also require ongoing monitoring and periodic deeper assessments.
Find Mobile App Security Gaps Before Attackers Do
Get expert guidance on mobile application security testing for your Android and iOS applications.
Request a Free DemoTalk to a Mobile Security ExpertFrequently Asked Questions About Mobile Application Security Testing
Secure Your Mobile Applications Before the Next Release
Assess your Android and iOS security posture with an enterprise mobile application security testing strategy.
Request a Mobile Security DemoSchedule a Consultation