Static Code Analysis Tools Provider for Secure Software Development
Find security vulnerabilities, coding defects, quality issues and compliance risks in source code before they reach production.
Evaluate enterprise static code analysis and SAST tools across development, CI/CD and secure SDLC workflows with Meteonic.
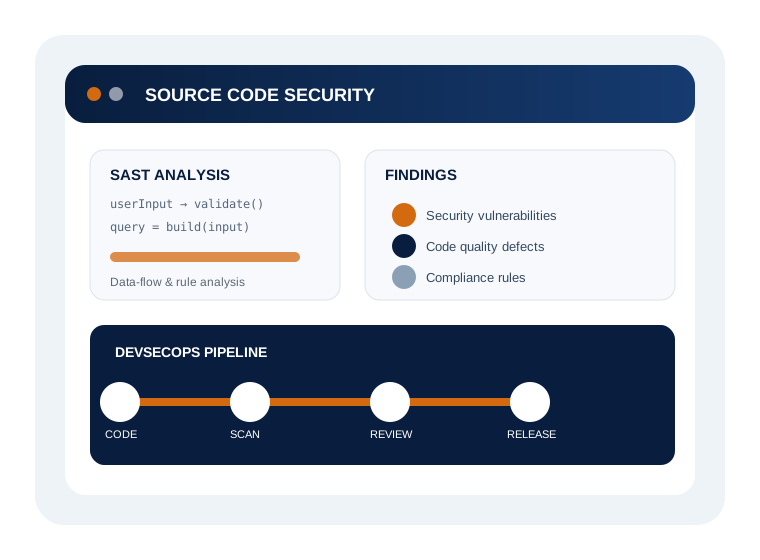
What Is Static Code Analysis?
Static code analysis is the automated examination of source code, bytecode or other code representations without executing the application. Static Application Security Testing (SAST) uses static analysis to identify security vulnerabilities and insecure coding patterns early in the software development lifecycle. It can also support code quality, coding-standard and compliance checks.
Why Enterprises Use Static Code Analysis Tools
Modern software teams need security feedback early enough for developers to fix issues while the code is still changing.
Detect Vulnerabilities Early
Identify insecure coding patterns such as injection risks, unsafe data flows, hardcoded secrets and other weaknesses before deployment.
Improve Source Code Quality
Find defects, code smells, complexity, duplication and maintainability issues that can increase technical debt.
Strengthen Secure SDLC
Bring security checks closer to development through IDE, pull-request and CI/CD integrations.
Support Compliance
Map findings and coding rules to applicable standards and organizational secure-coding policies.
Analyze Complex Codebases
Assess large, multi-language and legacy codebases with analysis suited to enterprise engineering environments.
Automate Security Gates
Run repeatable analysis during commits, pull requests, builds and releases to make code security measurable.
Static Code Analysis Capabilities to Evaluate
Security Vulnerability Detection
Analyze code paths and patterns for security weaknesses and prioritize findings for remediation.
Data Flow & Taint Analysis
Trace how potentially untrusted data moves through application logic to identify risky flows.
Code Quality & Defect Detection
Detect bugs, reliability issues, code smells, complexity and maintainability problems.
Secure Coding Standards
Evaluate code against organizational rules and relevant security or safety coding standards.
CI/CD & DevSecOps Integration
Integrate analysis into development pipelines so security feedback arrives before release.
Risk-Based Reporting
Use severity, context, ownership and remediation information to help teams focus on meaningful findings.
Static Code Analysis vs SAST: What Is the Difference?
Static code analysis is the broader practice of examining code without executing it. It can cover security, defects, architecture, complexity, coding standards and maintainability.
SAST is the application-security-focused use of static analysis to identify vulnerabilities in source code, bytecode or related representations. Enterprise programs may use both security-focused SAST and broader code-analysis capabilities depending on their engineering and compliance goals.
For an enterprise evaluation, check both
- Security vulnerability coverage
- Language and framework support
- Accuracy and finding context
- CI/CD and IDE integration
- Custom rules and standards
- Reporting, governance and scalability
Static Code Analysis Tools for Indian Enterprises
Engineering organizations in BFSI, automotive, healthcare, manufacturing, IT services and other regulated environments can use static analysis to embed security and quality controls into the software lifecycle.
Large Codebases
Assess complex repositories, legacy applications and multi-team development environments.
Regulated Development
Support secure coding policies, traceability and standards-driven development.
DevSecOps Pipelines
Automate analysis across source control, builds, pull requests and CI/CD workflows.
Security & Engineering
Give developers, AppSec teams and security leaders a shared view of code risk.
Static Code Analysis Tools Provider In India
Meteonic helps organizations evaluate and deploy enterprise static analysis, SAST and source-code intelligence technologies according to language, architecture, compliance and DevSecOps requirements.
Perforce Klocwork
Enterprise static analysis and SAST for complex software, with strong capabilities for security, reliability, coding standards and CI/CD workflows.
Explore KlocworkUnderstand by SciTools
Static analysis and code-comprehension capabilities for navigating large codebases, dependencies, metrics, coding standards and architecture.
Explore UnderstandCAST
Application intelligence and software health analysis to understand application portfolios, code health, technical debt and modernization priorities.
Explore CASTCheckmarx
Enterprise SAST for identifying security vulnerabilities in source code and integrating application security into development workflows.
Explore CheckmarxEmbold
Static code analysis combining security findings, code quality, anti-patterns, design insights, duplication and code metrics.
Explore EmboldKiuwan
SAST and code-security capabilities for identifying and prioritizing vulnerabilities with secure development and CI/CD workflows.
Explore KiuwanHow to Choose the Right Static Code Analysis Tool
There is no single SAST tool that fits every enterprise. Evaluate the technology against your actual codebase and development model.
1. Language Coverage
Check support for the languages, frameworks and build environments used by your teams.
2. Detection & Accuracy
Assess vulnerability coverage, context, false-positive handling and remediation guidance.
3. Developer Workflow
Look for IDE, pull-request, repository and CI/CD integrations that fit existing processes.
4. Enterprise Governance
Consider RBAC, reporting, policy controls, scalability, deployment and compliance requirements.
Static Code Analysis & SAST Topics We Cover
Questions About Static Code Analysis Tools
What are static code analysis tools?
They are software tools that inspect source code, bytecode or related code representations without executing the application to identify security, quality, reliability or compliance issues.
What is a SAST tool?
A SAST tool performs static application security testing to identify vulnerabilities and insecure coding patterns early in the software development lifecycle.
What is the difference between SAST and static code analysis?
Static code analysis is the broader category. SAST focuses specifically on application security vulnerabilities and secure coding risks.
Can SAST tools integrate with CI/CD?
Yes. Enterprise SAST tools can integrate with source control, IDEs, pull requests and CI/CD pipelines to automate security checks.
What vulnerabilities can static analysis detect?
Depending on the engine and rules, static analysis can detect issues such as injection risks, insecure data flows, unsafe memory usage, hardcoded secrets and other coding weaknesses.
Do static code analysis tools replace penetration testing?
No. Static analysis examines code without executing it. Dynamic testing, penetration testing and other security assessments identify different classes of risk and are complementary.
Which static code analysis tool should an enterprise choose?
The appropriate tool depends on programming languages, application architecture, security requirements, compliance standards, developer workflows, deployment model and enterprise scale.
Can Meteonic help with SAST tool selection in India?
Yes. Meteonic helps organizations evaluate enterprise static analysis and SAST technologies against their development environment and security objectives.
Find the Right Static Code Analysis Tool for Your Development Environment
Get an enterprise-focused SAST and static code analysis consultation from Meteonic. Discuss your languages, codebase, CI/CD environment and security requirements.
Request a Free SAST DemoTalk to an Expert